Coldcard Security Breach Deepens as Attacker Relocates $7.7M in Stolen Bitcoin Vaults
The perpetrator behind the massive Coldcard wallet exploit has systematically transferred $7.7 million, systematically draining funds from hundreds of structured vaults.
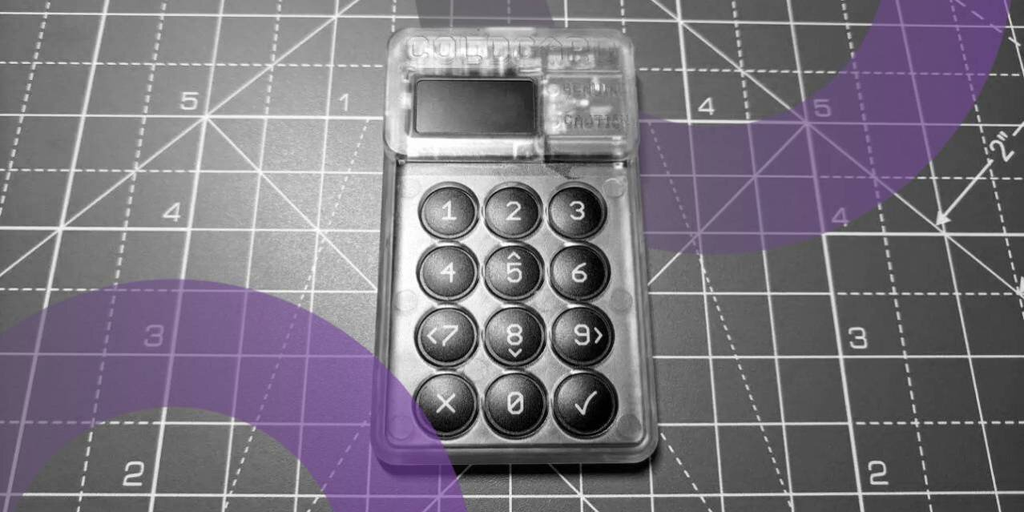
Source image: decrypt.co
decrypt.coThe Anatomy of an Ongoing Crypto Heist
The cryptocurrency security landscape has been thrown into turmoil following fresh on-chain movements tied to the major Coldcard hardware wallet exploit. Intelligence analysts and blockchain surveillance firms have confirmed that the primary wallet associated with the attack recently shifted $7.7 million worth of Bitcoin. This movement represents nearly half of the stolen capital amassed during the most recent phase of the breach, signaling that the threat actor is actively working to obscure and liquidate their ill-gotten gains.
According to forensic data, the hacker originally compartmentalized the stolen assets into 293 separate vaults. This calculated strategy was designed to complicate tracking efforts by mixing transactional flows and frustrating automated heuristic tools utilized by blockchain analytics providers. The attacker is currently emptying these fractionalized vaults in strict order of size, prioritizing the largest holdings first to maximize immediate liquidity extraction before smaller tranches are potentially flagged or frozen by centralized exchange compliance desks.
Implications for Digital Asset Custody and Hardware Security
The persistence and sophistication of this ongoing liquidation event highlight systemic risks within the self-custody ecosystem. While hardware wallets have long been touted as the gold standard for protecting private keys against online threats, incidents involving physical vulnerabilities or sophisticated supply-chain vectors continue to rattle investor confidence.
For high-net-worth individuals, family offices, and institutional allocators managing substantial digital asset treasuries, this event serves as a stark reminder that physical storage alone does not eliminate counterparty or operational risk. Security frameworks must evolve beyond simple offline storage to incorporate multi-signature configurations, time-locks, and advanced anomaly detection systems.
Market Sentiment and On-Chain Surveillance
The methodical dumping of millions of dollars in stolen Bitcoin creates distinct downward psychological pressure on market liquidity, albeit localized. As the funds travel through various obfuscation layers—including potential interactions with privacy mixers, cross-chain bridges, and over-the-counter (OTC) brokers—market participants are closely watching how centralized platforms respond.
- Exchange Monitoring: Major centralized exchanges have heightened automated surveillance on incoming deposits matching the specific cluster signatures tied to the Coldcard exploit.
- Miner Cooperation: Security coordinators are in active dialogue with prominent mining pools to orphan or flag transactions attempting double-spends or rapid mixing maneuvers.
- Regulatory Scrutiny: Financial watchdogs are using this high-profile incident to press for stricter compliance standards across hardware wallet manufacturers and open-source firmware distributors.
Strategic Takeaways for Investors and Market Participants
As the digital asset class matures, incidents of this magnitude directly influence corporate governance and risk assessment models. Investors must look beyond superficial security labels and demand rigorous, independently audited firmware transparency. Key indicators to monitor moving forward include:
The speed and efficiency with which blockchain analytics firms can tag and black-hole the remaining tranches of stolen capital.
Potential liability claims or remediation efforts directed at hardware manufacturers following large-scale architectural exploits.
Shifts in institutional preference toward multi-vendor multi-signature setups to mitigate single-point-of-failure risks inherent in standalone hardware devices.
Ultimately, the Coldcard hacker's methodical extraction of $7.7 million is more than an isolated cybercrime; it is a watershed moment forcing a comprehensive audit of how the cryptocurrency industry protects generational wealth against state-sponsored or elite-level independent threat actors.
Continue reading
Related coverage in Crypto
cointelegraph.com
Trump Schedules Third Memecoin Holder Dinner Amid Growing Corruption Scrutiny
President Trump is set to host his third exclusive memecoin dinner for top token holders at his Washington, DC golf club, drawing renewed ethical and market scrutiny.
3 min read
cointelegraph.com
50,000 Europeans Petition EU to Relax MiCA Stablecoin Reward Restrictions
A new 50,000-letter campaign is urging Brussels to ease stablecoin rewards restrictions during the MiCA review, aligning with broader central bank pushes.
2 min read
cryptonews.com
Dogecoin Eyes $1 Milestone as DogeOS Testnet Launch Sparks Utility Speculation
Dogecoin trades at $0.09447 as the DogeOS testnet goes live. Traders eye the $0.098 resistance and psychological $0.10 mark amid fresh utility potential.
2 min read
decrypt.co
Bitcoin Enters 'Uptober' Amid Fed Rate Hike Pressures and 5.3% Treasury Yields
Bitcoin enters its historically strongest month following a record September, yet rising Federal Reserve rate hike fears and 5.3% Treasury yields present major hurdles.
2 min read